Adversary Simulation
Emulate stages of an attack across IT and OT. Give Red and Blue Teams a concrete sequence to investigate and validate.
COMMAND & CONTROL / INDUSTRIAL SECURITY
Adversary Simulation. IT → OT pivoting. Industrial security research. A Command & Control framework built to test attack paths across converged IT and OT environments.
OFFENSIVE SECURITY INDUSTRIAL BY DESIGN
01 / THE FRAMEWORK
SCADAsploit combines IT offensive capabilities with modules designed for PLC, SCADA and other industrial systems. It supports penetration testing, Red Teaming and OT/ICS research through a distributed C2 architecture.
Follow an attack path beyond the enterprise network: identify assets, examine reachable industrial devices and test how defensive controls respond.
Emulate stages of an attack across IT and OT. Give Red and Blue Teams a concrete sequence to investigate and validate.
Identify industrial devices, map network relationships and collect device information to inform the assessment.
Staged and stageless beacons support operations in IT environments, providing the starting point for converged IT/OT assessments.
Explore reachable network paths from an IT foothold toward industrial devices. Test segmentation against an actual assessment path.
Use industrial modules to investigate devices and vulnerabilities, with the context needed to select the next test.
Protocol-aware modules support industrial research. Public examples include Modbus/TCP discovery and Schneider UMAS enumeration.
02 / FROM IT TO OT
An illustrative assessment sequence, from an authorized IT foothold to industrial security validation. Each engagement defines its own scope, access and operational constraints.
Establish the agreed entry point
Assess the enterprise foothold
Connect the assessment agent
Explore reachable systems
Cross the IT / OT boundary
Identify industrial assets
Test the scoped device
Review controls and response
03 / DISTRIBUTED BY DESIGN
The Remote Commander, teamserver and beacon separate operator interaction, C2 coordination and activity in the assessed environment.
Graphical client for framework operations.
Server-side sessions, modules and operator coordination.
Staged or stageless agent for remote operations.
Hosts, sessions and remote operations
Network pivot
PLC · SCADA · HMI · Remote I/O
INDUSTRIAL FOCUS
SCADAsploit’s research focus includes major industrial ecosystems. Capabilities depend on the device, protocol and module; vendor names are not a claim of universal product coverage.
04 / ADVERSARY SIMULATION
SCADAsploit brings an offensive sequence into a shared technical discussion. Red Teams execute scoped tests; SOC, Blue Team and OT security teams examine what their controls observed and how they responded.
Compare assessment activity with what defenders can observe.
Evaluate whether the intended network boundaries constrain the tested path.
Review investigation and response to improve the next defensive iteration.
THE INTERFACE / IN CONTEXT
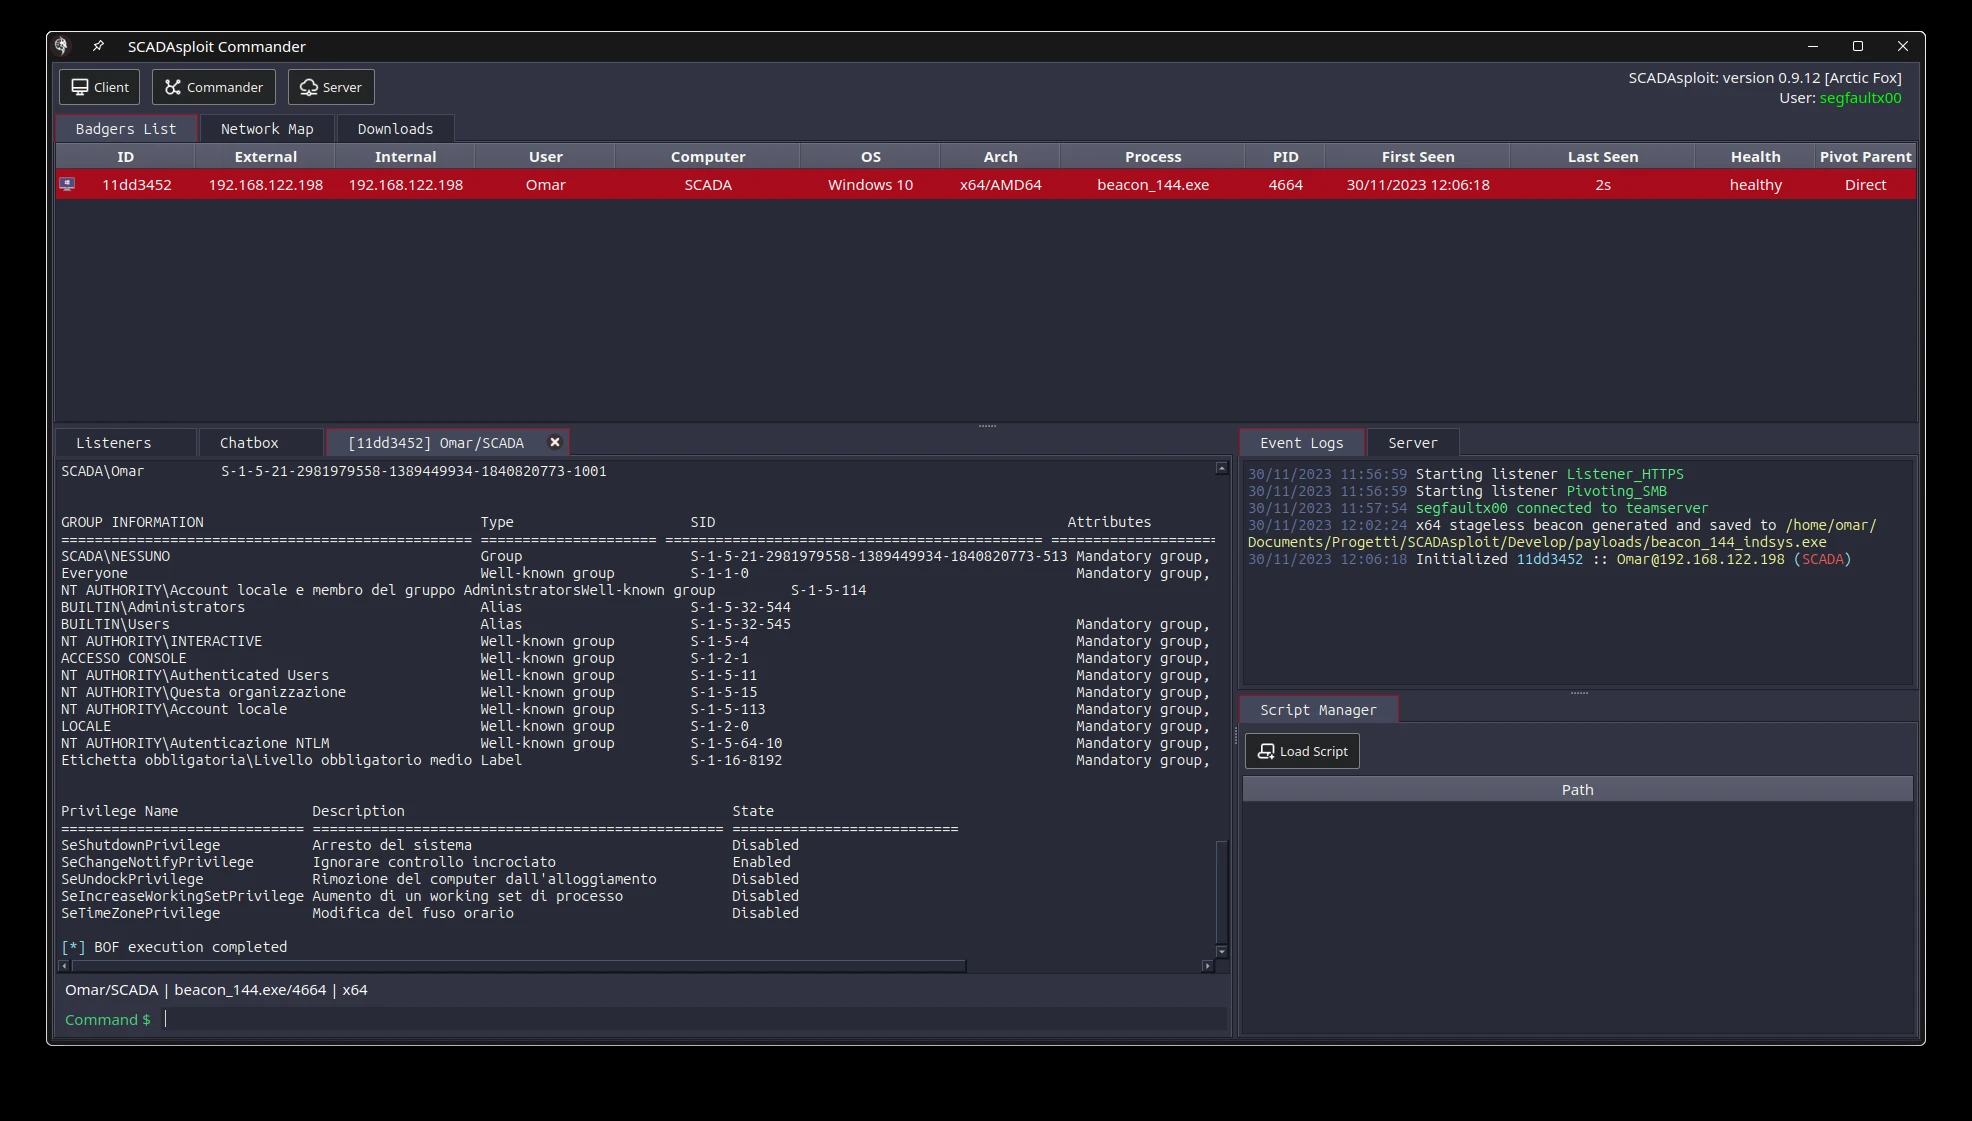
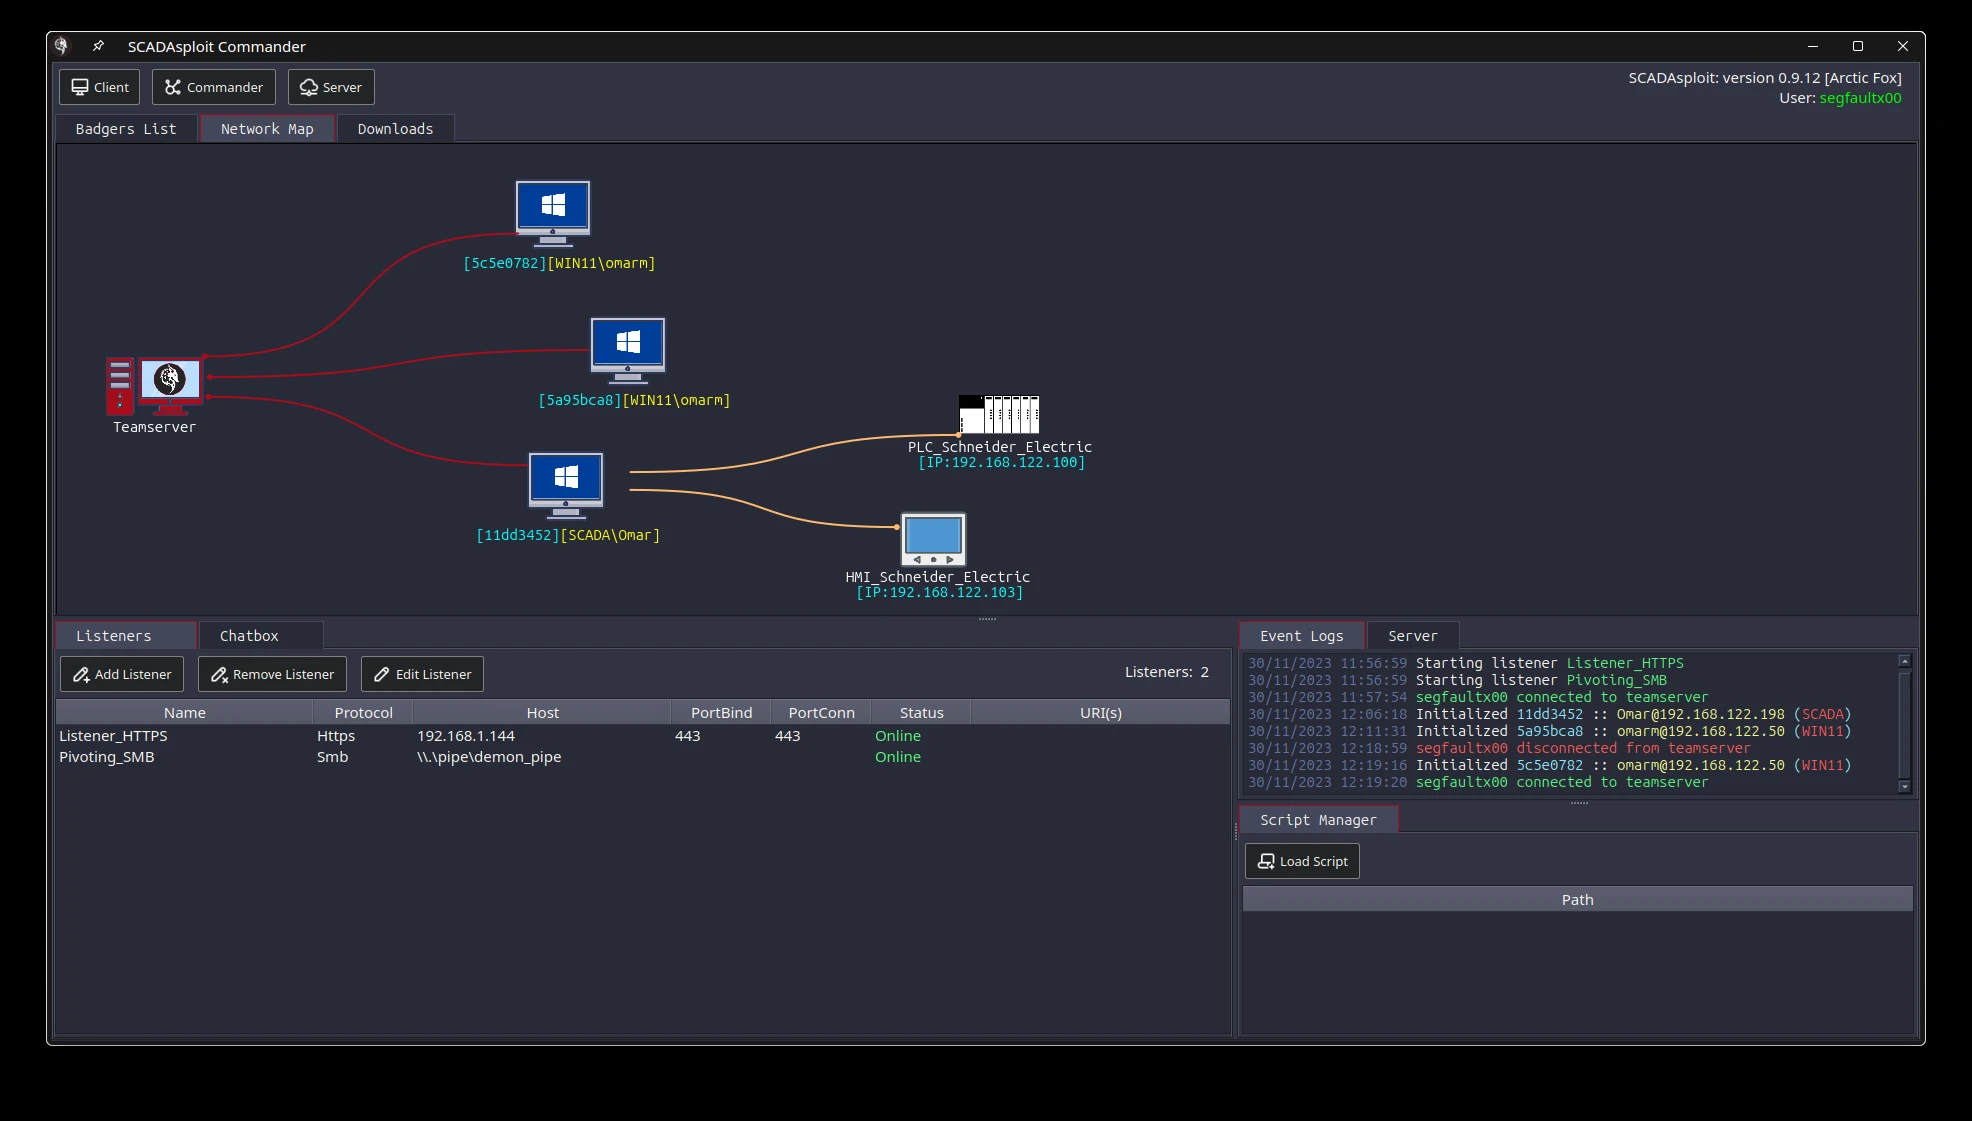
Explore the publicly documented interface. These screenshots show example environments, not live sessions.
REMOTE COMMANDER
A real view of the SCADAsploit graphical commander, showing connected nodes alongside operational panels.
01 / 03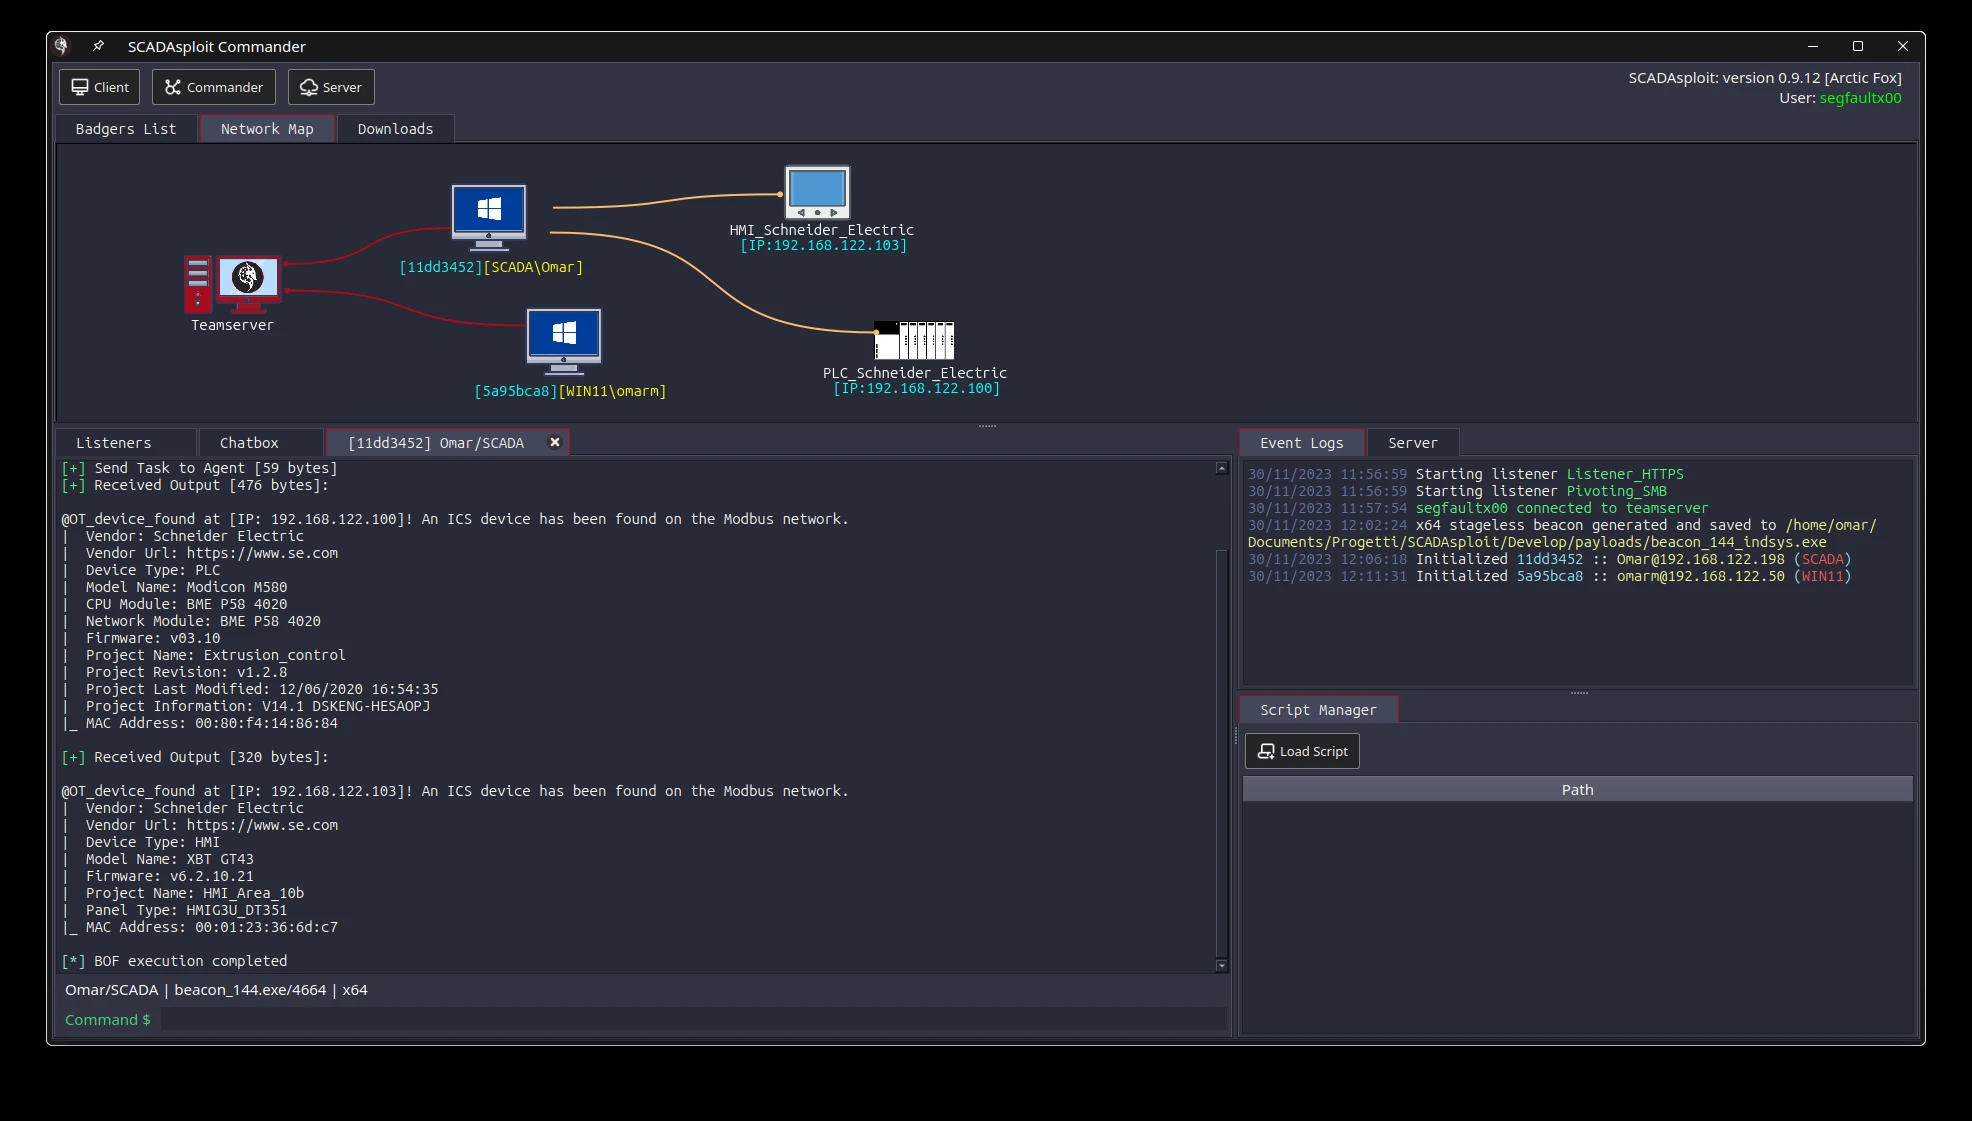
05 / WORKSHOPS
Technical training grounded in industrial systems and real protocols. Learn why a vulnerability exists, reproduce its effects in a controlled setting and understand the countermeasure.
Advanced · Hands-on
An intensive exploration of industrial attacks and their countermeasures. Work with ICS architecture, PLC internals and real protocols; use Python and C/C++ to investigate vulnerabilities and develop assessment tools.
OT security professionals and engineers familiar with ICS, programming and basic penetration testing tools.
Advanced · OT fundamentals required
Build practical knowledge of industrial cybersecurity, from information-security fundamentals to resilient architectures and incident response. Connect device protection with network design and industrial best practices.
Industrial system designers, PLC/SCADA programmers, network specialists and OT cybersecurity professionals.
Advanced · PLC programming required
Apply cybersecurity principles to PLC application software. Design more resilient control applications and diagnose the effects of cyber incidents on PLC program execution.
PLC programmers, maintenance technicians, system integrators, machine builders, plant operators and automation engineers.
06 / BUILT FROM INDUSTRIAL EXPERIENCE
SCADAsploit is created and developed by Omar Morando, Offensive OT Security researcher and Co-Founder & CTO of BlackFox. His background spans industrial automation, PLC/SCADA systems, embedded software and cybersecurity.
The continued development of SCADAsploit sits within Omar’s technology and research work in the BlackFox ecosystem.
Meet the creator ↗PRODUCT / RESEARCH / TRAINING
For questions about SCADAsploit, industrial security research, authorized assessments or advanced technical training.